 BYKO
Self-Custody Did Not Patch the Wallet
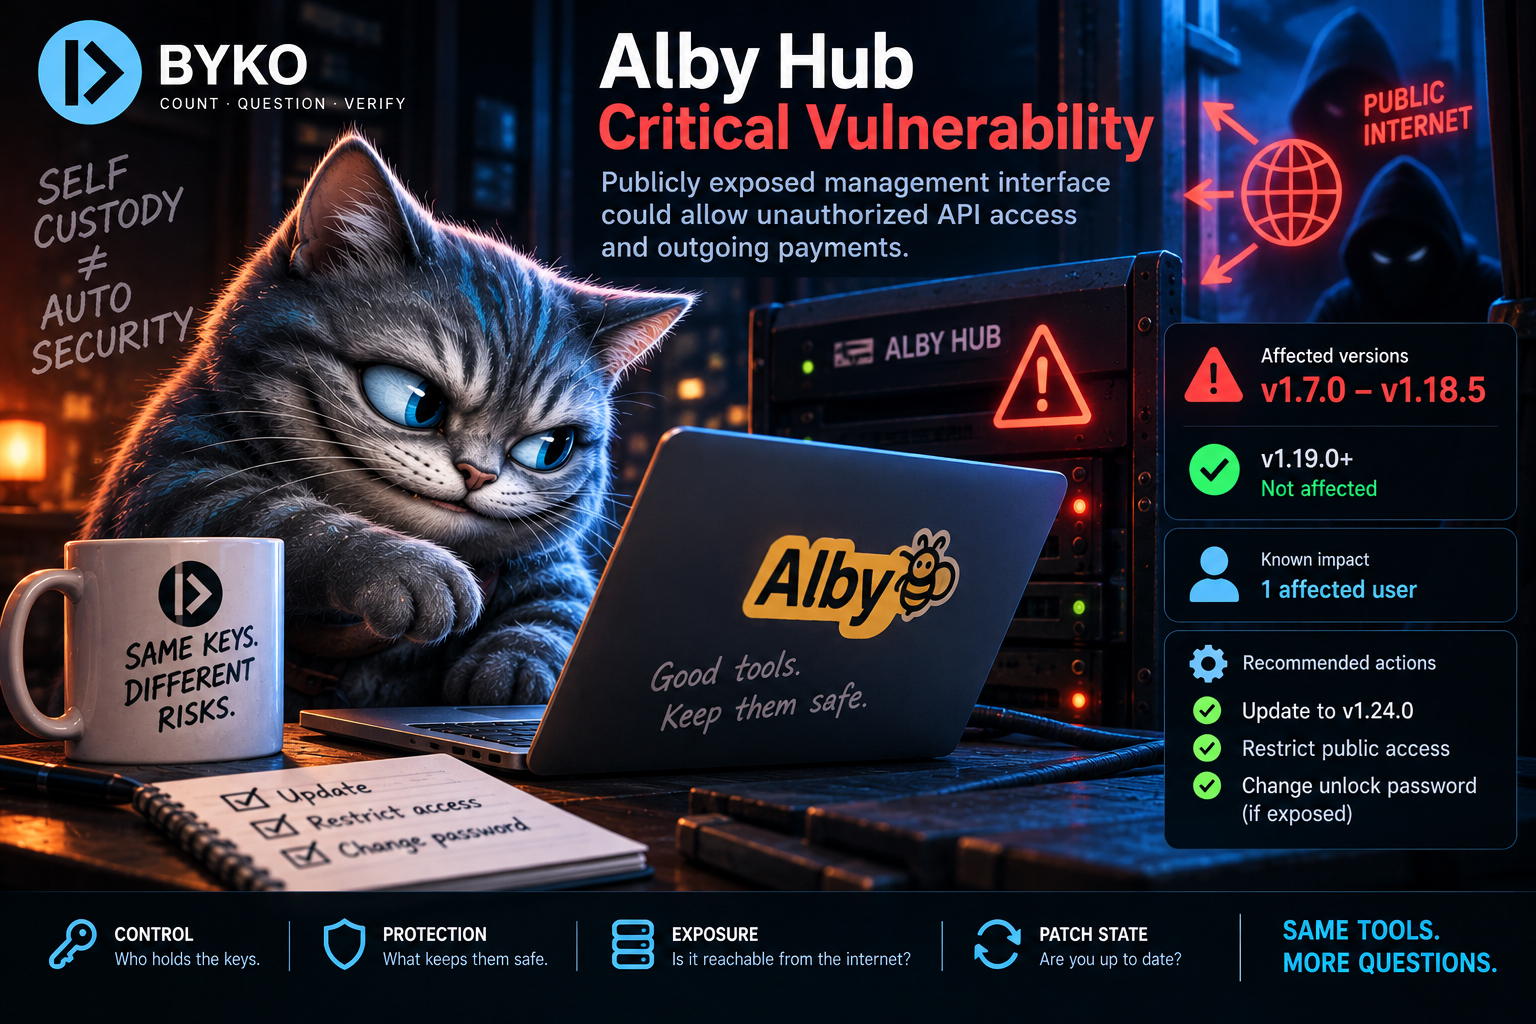
Alby disclosed a critical vulnerability in older Alby Hub versions when the wallet's management interface was reachable from the public internet. The flaw could allow unauthorized API access and outgoing payments. One affected user is known.
The affected range is v1.7.0 through v1.18.5. Alby says v1.19.0 and later are unaffected and recommends restricting public access, updating to v1.24.0, and changing the unlock password on previously exposed installations.
For BYKO, the useful distinction is between control and protection. Self-custody identifies who holds the keys; it does not certify the software, network exposure, or patch state protecting those keys. An immutable token contract can remain correct while the operational custody layer fails.
Sources: Alby, GitHub, The Hacker News, Bitcoin.com, CriptoNoticias.
Figures corrected after publication stay on the page: the old number is struck, not deleted, and the entry that fixed it is dated.